Unified Control Foundation
Map your controls once and satisfy requirements across NIST, HIPAA, TX-RAMP, CMMC, SOC 2, and more — without duplicating work for every framework.
Solutions
NorthStar connects your controls, frameworks, and evidence into a single compliance program — so your team spends less time managing spreadsheets and more time reducing risk.
How it works
NorthStar guides your organization through a repeatable process — from understanding your environment to demonstrating compliance across every applicable framework.
What you get
Map your controls once and satisfy requirements across NIST, HIPAA, TX-RAMP, CMMC, SOC 2, and more — without duplicating work for every framework.
Track control implementation status, evidence gaps, and remediation progress in real time — not just at audit time.
Organize and link supporting evidence directly to controls and requirements so your team is always prepared for assessments and audits.
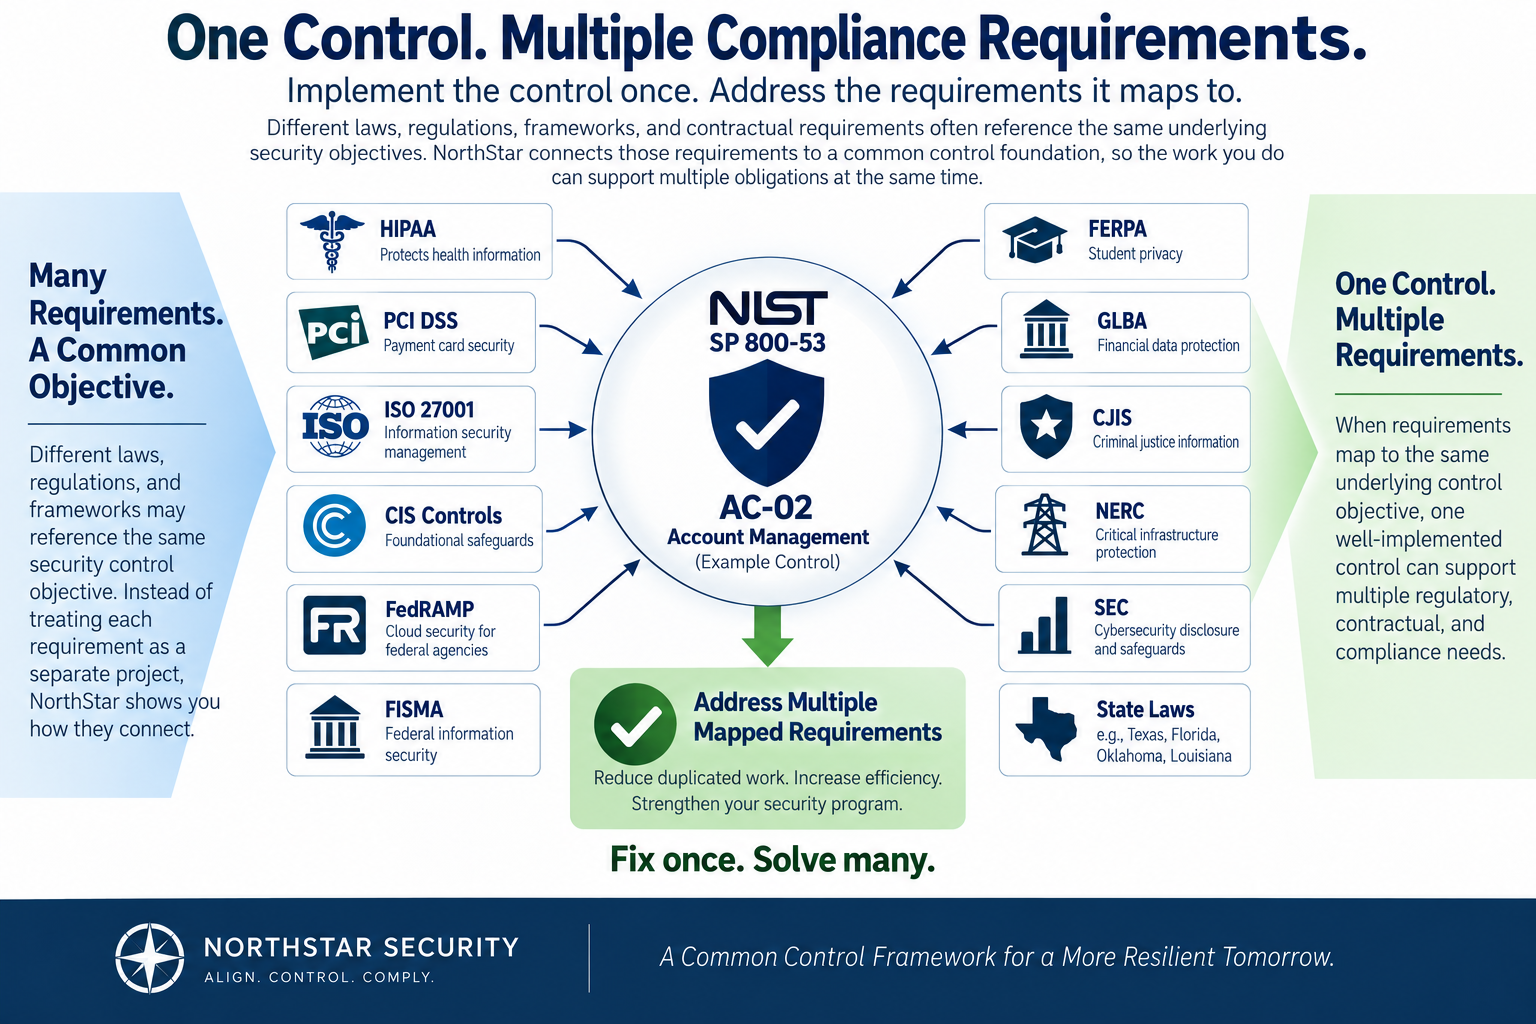
One control. Multiple compliance requirements.
Different laws, regulations, frameworks, and contractual requirements often reference the same underlying security objectives. NorthStar connects those requirements to a common control foundation, so the work you do can support multiple obligations at the same time.
One Control. Multiple Compliance Requirements.
Who we serve
NorthStar is designed for organizations that operate under multiple regulatory and contractual compliance obligations.
HIPAA, HITECH, and state privacy requirements.
GLBA, PCI DSS, and financial regulatory compliance.
TX-RAMP, FISMA, CMMC, and state agency requirements.
FERPA, GLBA, and institutional data protection obligations.
SOC 2, ISO 27001, and customer security requirements.
NERC CIP, NIST CSF, and sector-specific requirements.
Use cases
NorthStar provides a structured starting point — guiding your team through discovery, control mapping, and gap identification so you can build a defensible program from day one.
Stop maintaining separate spreadsheets for every framework. NorthStar maps your controls to all applicable requirements so one implementation satisfies many obligations.
Organize evidence, track control status, and generate reports that demonstrate your compliance posture — so audits become a confirmation of work already done.
Manage compliance programs across your entire customer portfolio from a single pane of glass — with tenant isolation, role-based access, and per-customer reporting.
Why it matters
Most organizations subject to regulatory compliance face overlapping requirements across multiple frameworks. HIPAA, NIST SP 800-53, TX-RAMP, CMMC, and SOC 2 all reference similar underlying security controls — but without a unified approach, teams end up duplicating effort across every framework they're subject to.
NorthStar's control foundation connects requirements across frameworks to a common set of controls. Implement the control once. Satisfy every requirement it maps to.
See how NorthStar's unified control foundation maps your existing controls to every framework you're subject to — and shows you exactly where the gaps are.
The platform
From system discovery to evidence management, NorthStar provides the structure your team needs to build, manage, and demonstrate a mature compliance program.
A connected approach
The NorthStar platform provides a structured environment for organizing compliance requirements, controls, and supporting documentation. When an organization needs additional expertise, NorthStar Professional Services can provide fractional executive leadership, security testing, program assessments, compliance readiness, risk assessments, and governance support. These offerings work together but do not depend on one another.
Fractional CISO and Fractional CIO services.
Penetration testing and vulnerability scanning.
Cybersecurity program, regulatory readiness, and security risk assessments.
Security policy and governance development.
See how NorthStar can help your organization build a structured, audit-ready compliance program across every framework you're subject to.