7 Steps for Mapping Internal Controls to NIST
Table of Contents
- Why Mapping Internal Controls to NIST Beats Starting From Scratch
- Step 1: Choose Your NIST Baseline and Version
- Step 2: Inventory Systems and Build a Control Inventory
- Step 3: Map Existing Controls with NIST Control Mapping Examples
- Step 4: Run a NIST Control Gap Analysis and Build a Remediation Plan
- Step 5: Document Mappings with an Internal Controls Mapping Template
- Step 6: Extend to NIST CSF Control Mapping and Crosswalks
- Step 7: Assign Owners, Collect Evidence, and Set a Testing Cadence
- Frequently Asked Questions
Last Updated: October 5, 2026
Why Mapping Internal Controls to NIST Beats Starting From Scratch
Mapping internal controls to NIST means linking the security measures you already operate to a recognized control catalog. Done well, one set of safeguards can support many frameworks, customer questionnaires, and audit requests at the same time.
The alternative—treating every framework as its own project—is where most programs lose time and confidence. Teams answer the same questions repeatedly, collect the same evidence more than once, and never build a reusable foundation. The result is overhead that grows with every new obligation instead of a program that scales.
A shared control foundation changes that dynamic. Map once, keep the mappings and evidence connected to risk and remediation, and new frameworks join the existing program rather than becoming new projects. That is the practical meaning of “fix once, solve many.”
Key takeaway: One control mapped to multiple frameworks replaces repeated assessments with a single, maintainable evidence set.
Step 1: Choose Your NIST Baseline and Version
Start with the right baseline. Every later mapping and gap decision inherits that choice. NIST SP 800-53 Rev. 5 is the current detailed control catalog. NIST also publishes SP 800-53B, which defines control baselines at low, moderate, and high impact levels.
• Low impact — limited potential harm if compromised.
• Moderate impact — serious harm; the common default for many enterprise and mid-market environments.
• High impact — severe or catastrophic harm.
NIST CSF 2.0 is complementary but serves a different purpose. Use the CSF as the organizing structure for the overall security program (Govern, Identify, Protect, Detect, Respond, Recover). Use SP 800-53 as the detailed control foundation that everything maps to. The two work together; they are not substitutes for each other.
Step 2: Inventory Systems and Build a Control Inventory
You cannot map controls to systems you have not listed. Build two inventories before detailed mapping begins:
• System / asset inventory — system name, business owner, data types and classification, impact level, hosting model, and key integrations.
• Control inventory — each existing safeguard, where it is implemented, who operates it, and any source framework it already supports.
A common mistake is skipping the asset inventory and mapping straight to an ideal target state. Map reality first. Gaps become visible and actionable only after the current state is clear.
Step 3: Map Existing Controls with NIST Control Mapping Examples
Mapping connects what you already do to a NIST control objective and records how completely you meet it. A concrete entry is more useful than abstract guidance.
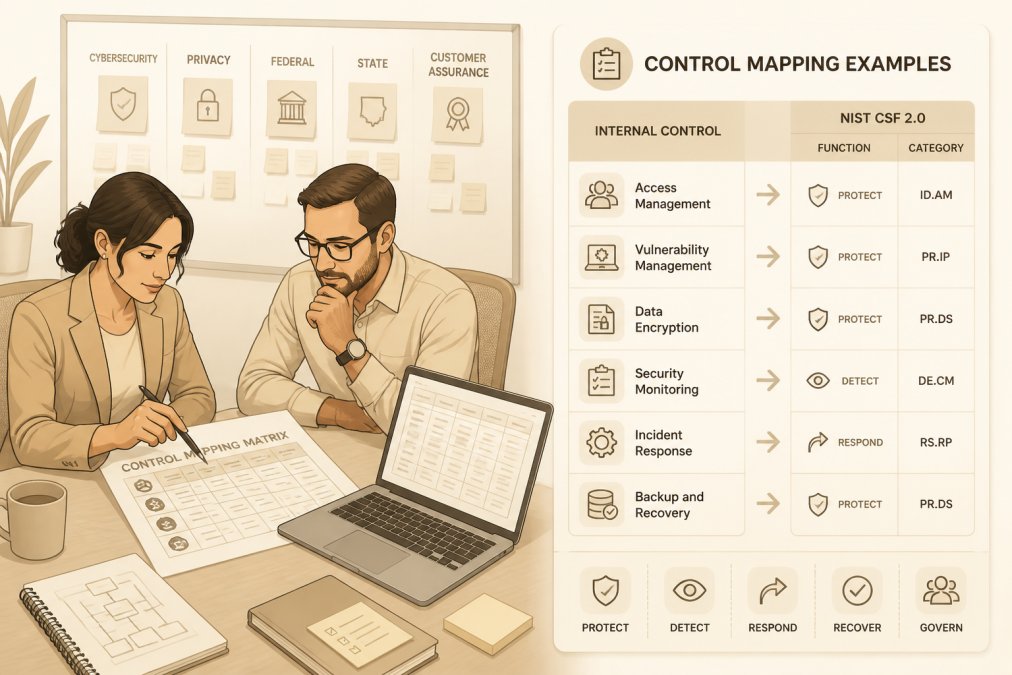
A Worked Mapping Entry
Example: Internal policy requires multi-factor authentication for all administrative access to production systems.
• Internal control ID: AC-ADMIN-MFA-01
• Internal control statement: MFA is enforced for all administrative access to production systems.
• NIST reference: IA-2, IA-2(1), IA-2(2)
• Mapping type: one-to-many (one internal control supports three NIST controls)
• Coverage: partial — MFA is enforced for admin accounts but not yet for service accounts or break-glass accounts.
• Evidence: identity-provider configuration export, conditional-access policy screenshot, quarterly access-review report.
• Owner: Director of Identity and Access Management
• Last tested / next test: Q3 access review; next scheduled for Q4.
• Rationale: The control addresses authentication for privileged users but does not yet extend to non-human accounts, so coverage of IA-2 is only partial.
The “partial” designation is one of the most important fields. It tells a reviewer—an auditor, a new team member, or you six months later—exactly where the mapping is incomplete so the gap can be tracked rather than hidden.
Handling One-to-One, One-to-Many, Many-to-One, and Partial Mappings
Most teams handle one-to-one mappings well and then get sloppy on everything else. Here is how the four common shapes differ:
Mapping Type | Example | How to Handle |
|---|---|---|
One-to-one | Your MFA policy maps to a single NIST authentication control | Direct link; record evidence and owner |
One-to-many | One quarterly access review satisfies three NIST access-control requirements | Link all three NIST controls to the single internal control; do not duplicate the evidence |
Many-to-one | Three internal controls (password policy, MFA, session timeout) all support one NIST control | Link each internal control separately; note which one carries the primary weight |
Partial | Logging covers servers but not cloud services | Map what exists, flag the uncovered scope explicitly, and open a gap item |
Partial and many-to-one mappings are where most teams get sloppy. Treating a partial mapping as full coverage is the single most common cause of a failed audit finding, the control exists, but it does not do what the NIST control requires across the full scope.
Step 4: Run a NIST Control Gap Analysis and Build a Remediation Plan
A NIST control gap analysis compares your mapped controls against the chosen baseline to find what is missing, weak, or only partially covered. The output is a list of control gaps, each tied to a risk, a remediation owner, and a target date.
Classify the Gap Before You Score It
Not every gap is the same kind of problem, and treating them alike leads to misallocated effort. Most programs sort gaps into four buckets:
- • Missing control — no internal control maps to the NIST requirement. Usually highest risk and highest effort.
• Partial coverage — a control exists but does not cover the full required scope (for example, logging on servers but not cloud workloads).
• Documentation gap — the control operates, but policy language or evidence is incomplete. Often the fastest to close.
• Design gap — the control exists and is documented but does not actually meet the current NIST control objective.
Score Each Gap on Likelihood and Impact
Once classified, score residual exposure on two axes: likelihood that the gap leads to a real security or compliance failure, and impact if it does. A simple high/medium/low scale is sufficient for most programs and produces a natural priority order:
• High likelihood + high impact → remediate first.
• High likelihood + low impact → quick wins (often documentation or configuration).
• Low likelihood + high impact → plan and schedule; these are the gaps that surface during audits.
• Low likelihood + low impact → accept, monitor, and revisit at the next review cycle.
A frequent pattern is over-investing in easy, low-likelihood gaps while high-impact partial-coverage items remain open because they require cross-team coordination. Score first, then sequence the work.
Build the Remediation Plan
Every gap item should carry enough structure to survive contact with an audit or leadership review:
• Gap ID and linked NIST control reference
• Gap classification (missing, partial, documentation, design)
• Likelihood and impact scores
• Specific remediation action (not a vague goal)
• Named accountable owner (a person, not only a team name)
• Target date and current status
• Verification method — how closure will be confirmed
Sequence so that high-impact partial-coverage gaps and missing controls on high-impact systems come first. Documentation gaps can often be batched. Design gaps frequently require policy or architecture changes and should be scheduled with the teams that own those systems.
Track Mapping Quality Over Time
Gap analysis is not a one-time event. Track a small set of metrics so you can see whether your mapping program is actually improving:
- Coverage rate: percentage of baseline controls with at least one mapped internal control.
- Full-coverage rate: percentage of mapped controls tagged as full rather than partial or planned.
- Unmapped controls: count of baseline controls with no mapping at all.
- Stale mappings: count of mappings not re-tested within their scheduled cadence.
- Open remediation items: count and average age, broken out by severity.
These five numbers tell you more about the health of your mapping program than any single audit result. Review them at the same cadence as your control testing, and use them to justify remediation budget when leadership asks why the work matters.
Step 5: Document Mappings with an Internal Controls Mapping Template
An internal controls mapping template keeps every mapping consistent and auditable. At minimum, it needs these columns:
- Control ID and NIST control reference
- Control description and source framework
- Mapping type (one-to-one, one-to-many, partial)
- Control owner and system
- Evidence location and last test date
- Coverage status and notes
A reusable matrix beats a folder of spreadsheets. It becomes your compliance checklist and your audit readiness view in one place.
Step 6: Extend to NIST CSF Control Mapping and Crosswalks
Once controls are mapped to the SP 800-53 foundation, the next layer is alignment to the NIST Cybersecurity Framework functions (Govern, Identify, Protect, Detect, Respond, Recover). This is not a second mapping exercise from scratch; it is an additional organizing view on top of the same control foundation.
Crosswalks to other standards (SOC 2, ISO 27001, privacy frameworks, federal and state requirements, customer questionnaires) follow the same principle: each new framework maps onto the existing control catalog rather than becoming a separate project. When a control is satisfied and evidenced for the foundation, that work can support every framework that references it.
This is how organizations move from running parallel compliance efforts to operating one connected security program. New obligations join the program; they do not restart it.
Step 7: Assign Owners, Collect Evidence, and Set a Testing Cadence
A mapping without an owner is a mapping that rots. Assign a control owner to every control, then set how often each one gets tested and re-evidenced.
- Control owner: accountable for the control working
- Evidence: the artifact that proves it, stored in one place
- Testing cadence: how often you re-check, based on risk
Continuous monitoring beats annual scrambles. Review mappings quarterly, re-test high-risk controls more often, and update the matrix when systems change.
Frequently Asked Questions
What are the 7 steps for mapping internal controls to NIST?
The seven steps are: choose your NIST baseline and version, inventory systems and build a control inventory, map existing controls to NIST requirements, run a gap analysis and build a remediation plan, document mappings with a template, extend to NIST CSF crosswalks, and assign owners with evidence and testing cadence. Each step builds on the last, so skipping the baseline or inventory step makes later mapping unreliable and hard to defend during audits.
Can one internal control map to multiple NIST requirements?
Yes, and this is common. A single access control policy may satisfy parts of NIST SP 800-53 AC-2, AC-3, and AC-17, plus NIST CSF PR.AC-1 and PR.AC-4. These one-to-many mappings are legitimate when you document the rationale and evidence for each linkage. The risk is over-claiming: a control that only partially meets a requirement should be flagged as partial, not full, so your gap analysis stays accurate.
What evidence should you collect to validate a NIST control mapping?
Collect evidence that proves the control operates, not just that it exists. Useful evidence includes policy documents with version history, configuration screenshots, access review logs, training completion records, and ticket histories showing remediation. Store evidence against the control record with an owner and review date. During audits, this reduces back-and-forth because reviewers can trace each NIST requirement to a specific artifact and the person accountable for it.
How often should an organization review its NIST control mappings?
Review mappings at least annually, and again whenever a system changes, a new framework applies, or an audit finding emerges. High-change environments such as cloud platforms may need quarterly reviews. Pair the review with continuous monitoring so control effectiveness is checked between formal cycles. The goal is to keep the mapping matrix current enough that a customer questionnaire or auditor request does not trigger a scramble to reconstruct what applies.
Most teams do not fail at mapping because the work is hard. They fail because they map once, then let the matrix drift while systems change underneath it. NorthStar Intelligence Portal keeps requirements, controls, risk, evidence, and remediation in one operating view, so your mappings stay current and your evidence stays reusable. Request a demo and see your security posture without rebuilding reporting from scratch.